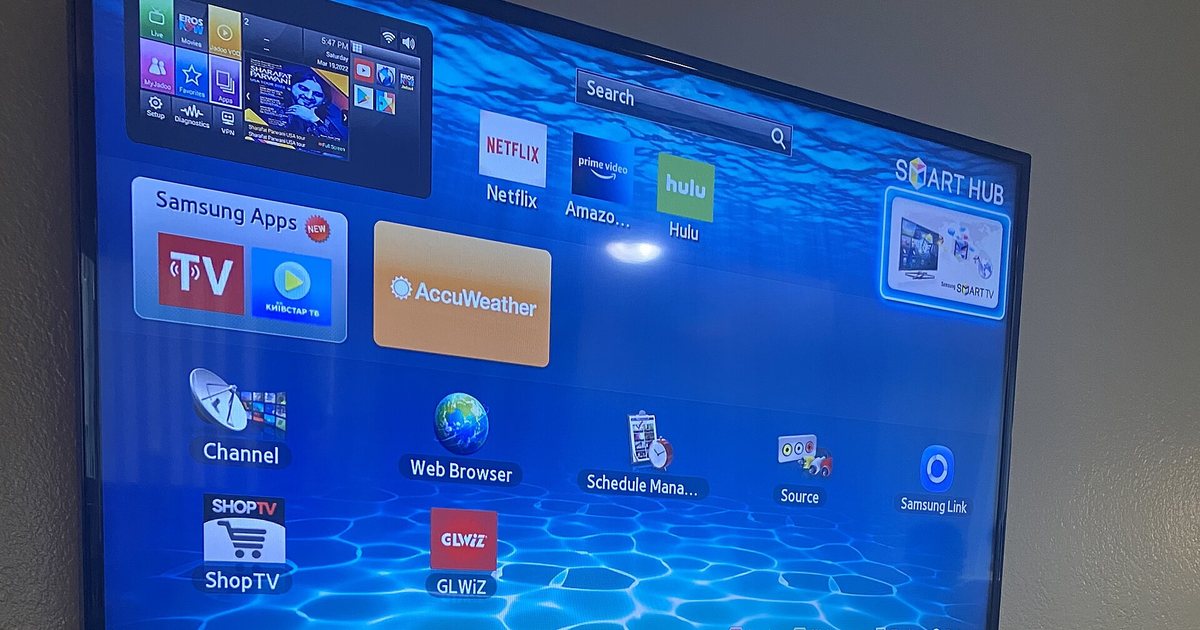
Photo: Samsung Smart TV 2012 (E-Series).jpg · Dancingpolishcow · CC BY-SA 4.0 · cropped (file photo)
A security researcher noticed targeted ads on a 2025 Samsung TV and exploited zero-day flaws to dismantle its Tizen operating system. The teardown triggered a viral online panic over smart TV privacy and potential security flaws.
What happened with the Samsung TV privacy findings
Between October 21 and October 25, 2026, a cybersecurity researcher using the online handle @log4j published a series of posts on X detailing a reverse-engineered 2025 Samsung Smart TV. After gaining administrative access through zero-day vulnerabilities, the researcher reported discovering what they called PRIVACY HORROR inside the Tizen operating system.
The findings detailed automated content recognition, geolocation tracking, continuous network mapping, and cross-device identification for targeted ads. The researcher claimed that TVs without built-in microphones seek out and use connected soundbars or Bluetooth devices to record ambient audio, while the power LED state can be artificially altered.
Is the Log4j vulnerability claim true?
The viral claim that Samsung Smart TVs currently suffer from a Log4j software flaw is false. The entire search panic comes from a misunderstanding of the researcher's username, @log4j, rather than a newly discovered software bug in TV firmware.
Samsung did patch actual Log4j software vulnerabilities back in December 2021, but those fixes applied to its Knox cloud infrastructure rather than television firmware. As for the researcher's privacy findings, full technical verification remains pending until a complete write-up is published, though Samsung documents audio sensors on 2025 models for SmartThings features like dog bark detection.
| Viral Claim | Verified Fact |
|---|---|
| Log4j software bug in TV firmware | False: Trend comes from researcher handle @log4j |
| Always-on microphone background recording | Unverified: Code shared, full lab audit pending |
| Historical Knox cloud Log4j vulnerability | True: Samsung patched Knox cloud services in Dec 2021 |
Why it matters to smart TV owners
If these technical findings are fully verified, Samsung Smart TVs collect extensive personal data from living rooms without explicit user awareness. The researcher claims Samsung utilizes automated content recognition to send user viewing data to a network of 400 potential advertising partners.
The report also links this heavy background processing to user complaints about sluggish TV performance. Processing screenshots, analyzing continuous audio, and running local AI models consume hardware resources that would otherwise keep the television user interface responsive.
What to watch next
The researcher @log4j is preparing a comprehensive technical write-up detailing the reverse-engineering methodology and code exploits. This document will allow independent cybersecurity laboratories to audit and attempt to replicate the claims. As of current reports, Samsung has not released an official comment regarding these privacy allegations for its 2025 Smart TV models.
FAQ
Did Samsung Smart TVs catch a Log4j virus?
No. The search spike was caused by a security researcher named @log4j publishing privacy findings, not a software bug.
Is my Samsung Smart TV secretly recording audio?
A researcher published code indicating background audio scanning, but these claims are currently awaiting independent laboratory verification.
Sources
tomshardware.comtomshardware.compasqualepillitteri.itpasqualepillitteri.itdaily.devdaily.devreddit.comreddit.comshiftdelete.neten.shiftdelete.netResearched from public reporting (including Korean-language sources) and written with AI assistance. Check the original articles for details.